Sentinel Strategy Group LLC | Effective Date: September 15, 2026 | Last Updated: September 15, 2026 | Version: 1.1
1. About This Policy
Sentinel Strategy Group LLC (“Sentinel,” “the Firm,” “we,” “us,” or “our”) is a consulting practice headquartered in Chicago, Illinois, providing AI deployment strategy, privacy governance, business consultancy, policy evaluation, and education and training services to clients in Illinois and across the United States.
This Privacy Policy explains how we collect, use, disclose, and safeguard personal information when you:
- visit sentinelstrategygroup.org (the “Site”);
- submit a contact, inquiry, or appointment request form;
- subscribe to our newsletter or other communications;
- engage us for professional services, or work for or with an organization that does;
- apply for a role with us, or otherwise correspond with us by email or telephone.
This Policy does not apply to: (a) personal information we process on behalf of a client under an engagement agreement (see Section 3); or (b) third-party websites, platforms, or services we link to.
2. Summary of Key Points
Do you sell my personal information?
No. We do not sell personal information, and we do not share it for cross-context behavioral advertising or targeted advertising, as those terms are defined under U.S. state privacy laws.
Do you collect sensitive personal information?
We do not seek it. We do not collect biometric identifiers or biometric information, precise geolocation, or government identifiers through the Site.
Do you use my data to train AI models?
See Section 8. We configure enterprise AI vendor settings to exclude client confidential information and personal data from third-party model training.
Can I ask you to delete my data?
Yes. We extend core privacy rights to every individual, regardless of where you live. See Section 11.
Who do I contact?
info@sentinelstrategygroup.org — see Section 19.
This summary is provided for convenience only. The full text of this Policy governs.
3. Two Different Roles: Our Data and Client Data
The Firm handles personal information in two distinct capacities. The distinction determines which rules and which agreements apply.
a) Where the Firm acts as a controller — this Policy applies. Information for which we determine the purposes and means of processing: website visitor data, inquiries, prospective client contacts, newsletter subscribers, appointment requests, vendor and business contacts, and job applicants.
b) Where the Firm acts as a processor or service provider — this Policy does not apply. In the course of an engagement, a client may give us access to personal information from its systems, records, or workforce — for example, during data mapping, a gap assessment, a data protection impact assessment, a policy evaluation, or a training exercise. In those circumstances:
- The client remains the controller and determines how that data is used;
- We process it only on the client’s documented instructions, under the engagement agreement and any applicable data processing addendum;
- We do not use it for our own purposes, do not sell it, and do not retain it beyond what the engagement and our records obligations require;
- Individuals wishing to exercise privacy rights over that data should contact the client organization directly. If you contact us instead, we will refer your request to the relevant client unless we are independently required by law to act on it.
The Firm also observes professional confidentiality obligations to its clients that operate independently of, and in addition to, the obligations in this Policy
4. Personal Information We Collect
4.1 Information you provide directly
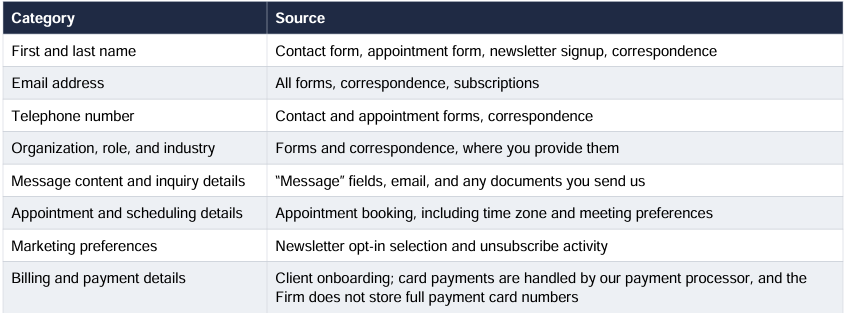
Please do not submit confidential, privileged, health, or otherwise sensitive information through our website forms. Use the form to describe the shape of the problem; we will arrange a secure channel before you send anything sensitive.
4.2 Information collected automatically
When you visit the Site, we and our service providers may automatically collect:
- IP address and approximate location derived from it, at the city or region level;
- Browser type and version, device type, operating system, and screen settings;
- Pages viewed, referring and exit pages, links clicked, and time spent on the Site;
- Date and time of access, and general usage and diagnostic data;
- Cookie and similar-technology identifiers, as described in Section 9.
4.3 Information from other sources
We may receive business contact information from: our clients and their personnel; professional networking platforms and public professional directories; conference and event organizers where you have interacted with us; referral sources; and publicly available business registries and regulatory filings.
4.4 Statutory categories under California law
For purposes of the California Consumer Privacy Act (“CCPA”), we collect or have collected in the preceding twelve months the following statutory categories:
- Identifiers — name, email address, telephone number, IP address;
- Customer records information (Cal. Civ. Code § 1798.80) — name, telephone number, contact details, billing information;
- Commercial information — services inquired about or purchased, engagement history;
- Internet or other electronic network activity information — browsing and interaction with the Site;
- Professional or employment-related information — employer, job title, work history, application materials;
- Inferences drawn from the above, such as likely service interest.
We do not knowingly collect biometric information, precise geolocation, sensitive personal information as defined by the CCPA, or the personal information of minors under sixteen.
5. How We Use Personal Information
We use personal information for the following business purposes:
- Responding to inquiries — replying to contact form submissions, scheduling and conducting introductory calls, and following up. We aim to respond within two business days.
- Delivering services — scoping, performing, and administering engagements, including diagnostics, framework development, policy drafting, evaluation, and training.
- Business administration — invoicing, payment, accounting, conflicts and independence checks, insurance, and records management.
- Communications — sending newsletters, insights, and updates where you have opted in, with an unsubscribe link in every message.
- Site operation and improvement — maintaining, securing, measuring, and improving the Site and its content.
- Recruiting — evaluating applications, conducting interviews, and, with your consent, checking references.
- Security and integrity — detecting, investigating, and preventing fraud, abuse, unauthorized access, and other malicious activity.
- Legal and regulatory compliance — complying with applicable law, responding to lawful requests, establishing or defending legal claims, and enforcing our agreements.
Legal bases
We rely on: your consent for marketing communications; the performance of a contract, or steps taken at your request before entering one, for engagements and inquiries; our legitimate business interests in Site security, service improvement, and proportionate business development; and our legal obligations.
6. No Sale or Sharing of Personal Information
The Firm does not sell personal information for monetary or other valuable consideration, and does not share personal information for cross-context behavioral advertising or targeted advertising, as those terms are defined under the CCPA and the comprehensive privacy statutes of other states, including Colorado, Connecticut, Virginia, Texas, Oregon, Montana, Delaware, Iowa, Nebraska, New Hampshire, New Jersey, Tennessee, Minnesota, Maryland, Indiana, Kentucky, Rhode Island, and Utah.
We have not sold or shared personal information in the preceding twelve months, including the personal information of consumers under sixteen.
We do not engage in profiling in furtherance of decisions that produce legal or similarly significant effects concerningany individual.
We do not disclose personal information to data brokers, advertising networks, or list resellers.
7. When We Disclose Personal Information
We disclose personal information only in the circumstances described below, and never for a purpose incompatible with the purpose for which it was collected.
a) Service providers and processors. We use a limited number of vendors, each bound by contract to process data only on our instructions, to maintain confidentiality and appropriate security, and to delete or return data at the end of the relationship. The categories of service provider we use are:
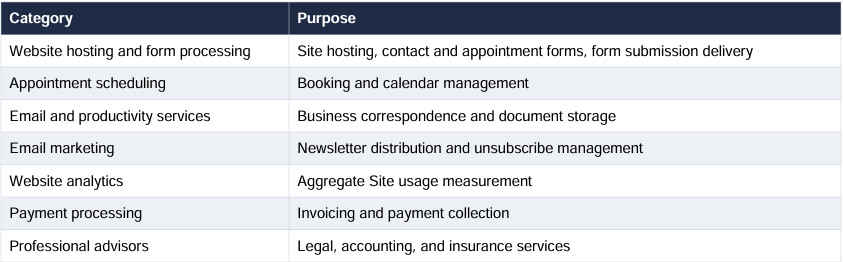
Our Site is hosted by Webbefy, and form submissions made through the Site are processed within that hosting environment. A current list of named service providers is available on written request to the address in Section 19.
b) Clients. Where you contact us in connection with an existing engagement, we may share your correspondence with the client organization involved.
c) Legal and regulatory. We may disclose personal information where we reasonably believe disclosure is required to comply with a law, subpoena, court order, or governmental request; to enforce our agreements; or to protect the rights, property, or safety of the Firm, our clients, or others. We will narrow the scope of any such disclosure to what is legally required, and where permitted by law we will notify the affected individual or client organization.
d) Business transfers. In connection with a merger, acquisition, financing, reorganization, or sale of assets, personal information may be transferred as a business asset. Any successor will remain bound by this Policy or will provide notice and choice before materially different treatment.
8. Artificial Intelligence
The Firm exercises commercially reasonable efforts to configure enterprise-grade AI vendor settings to exclude client confidential information and personal data from third-party model training, but makes no warranty that vendors honor such settings and disclaims liability for vendor non-compliance or output errors. AI is used internally only with confidentiality controls and redaction where feasible, and never for significant legal or financial decisions without human review and override authority. Client-directed AI use is governed solely by the engagement agreement, and any AI output is non-binding “AS IS” material requiring independent verification. The Firm shall review its AI configurations quarterly and provide, upon request, a redacted attestation of current opt-out status without disclosing privileged materials. TOTAL LIABILITY UNDER THIS CLAUSE SHALL NOT EXCEED THE LESSER OF FEES PAID IN THE PRIOR TWELVE MONTHS OR $5,000, WITH NO LIABILITY FOR CONSEQUENTIAL DAMAGES OR VENDOR-RELATED LOSSES.
9. Cookies and Similar Technologies
The Site uses cookies and similar technologies, including:
- Strictly necessary cookies — required for the Site to function, including form submission, security, and load balancing. These cannot be disabled through the Site.
- Functional cookies — remember preferences such as language or region.
- Analytics cookies — help us understand aggregate Site usage, including which pages are visited and how visitors arrive.
We do not use advertising or cross-site tracking cookies.
- Your choices. Most browsers allow you to refuse or delete cookies through their settings. Disabling strictly necessary cookies may prevent parts of the Site, including our forms, from working.
- Global Privacy Control and universal opt-out signals. We honor the Global Privacy Control (“GPC”) and other recognized universal opt-out preference signals transmitted by your browser or device. Because we do not sell or share personal information for targeted advertising, an opt-out signal does not change how we handle your data, but we recognize and respect it regardless.
- Do Not Track. There is no consistent industry standard for responding to browser “Do Not Track” signals. We do not track visitors across third-party websites, and we treat the Global Privacy Control as our recognized opt-out mechanism.
10. Data Retention
We retain personal information only as long as necessary for the purposes described in this Policy, or as required by law, professional obligations, or our records management schedule.
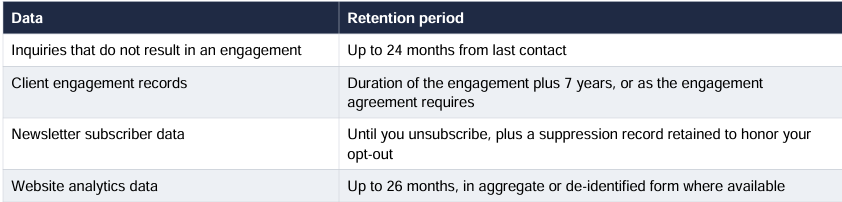
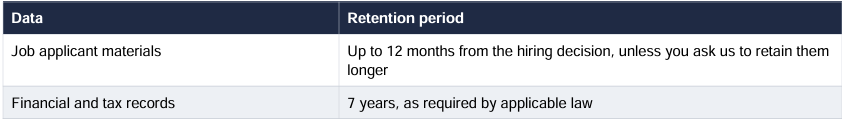
When retention is no longer justified, we securely delete, destroy, or irreversibly de-identify the information.
11. Your Privacy Rights
The Firm extends the following rights to every individual who contacts us, regardless of state of residence. Certain states grant these rights as a matter of law; we apply them uniformly.
You may request to:
- Know and access — confirm whether we process personal information about you, and obtain a copy of it together with the categories of sources and recipients.
- Correct — have inaccurate personal information corrected.
- Delete — have your personal information deleted, subject to exceptions including legal retention obligations and existing engagement records.
- Port — receive a copy in a portable, readily usable format where technically feasible.
- Opt out — of any sale, sharing for targeted advertising, or profiling with legal or similarly significant effects. We do not engage in these activities, and the right stands regardless.
- Withdraw consent — including unsubscribing from marketing communications at any time.
- Non-discrimination and non-retaliation — we will not deny services, charge different prices, or provide a different quality of service because you exercised a privacy right.
How to submit a request
Email info@sentinelstrategygroup.org with the subject line “Privacy Request,” or write to us at the address in Section 19. Identify the right you wish to exercise and provide enough information for us to locate your records.
Verification
To protect your data, we will verify your identity before acting, typically by confirming information already in our records or by correspondence from the email address associated with the request. We may decline requests we cannot reasonably verify. Information provided for verification is used only for that purpose and is not retained for any other use.
Authorized agents
An authorized agent may submit a request on your behalf with written permission signed by you, or with a valid power of attorney. We may contact you directly to confirm the authorization.
Timing
We will acknowledge requests promptly and respond substantively within forty-five (45) days. Where reasonably necessary, we may extend by an additional forty-five (45) days and will notify you of the extension and the reason within the initial response period.
Right to appeal
If we decline your request, we will explain why. You may appeal by replying to our response with the subject line
“Privacy Appeal.” We will respond to appeals in writing within sixty (60) days, explaining the reasons for our decision.
If an appeal is denied, you may submit a complaint to the Attorney General of your state.
12. State-Specific Disclosures
12.1 Illinois
Illinois does not currently have a comprehensive consumer privacy statute. The following Illinois laws apply to our operations:
- Biometric Information Privacy Act (BIPA), 740 ILCS 14. The Firm does not collect, capture, purchase, receive through trade, or otherwise obtain biometric identifiers or biometric information — including fingerprints, retina or iris scans, voiceprints, or scans of hand or face geometry — from Site visitors, clients, or personnel. We do not use facial recognition, voice analysis, or biometric authentication in our services. Should this change, we will obtain written consent and publish a biometric retention and destruction schedule before collecting any such data.
- Personal Information Protection Act (PIPA), 815 ILCS 530. In the event of a breach of the security of the system involving unencrypted personal information of Illinois residents, we will notify affected individuals in the most expedient time possible and without unreasonable delay, and will make any required notification to the Illinois Attorney General.
- Right of Publicity Act, 765 ILCS 1075. We do not use any individual’s name, image, likeness, or voice for commercial purposes without written consent.
12.2 California
In addition to the rights described in Section 11, California residents have the following:
- Notice at collection. The categories of personal information we collect, the purposes for which they are used, and our retention practices are described in Sections 4, 5, and 10. We do not sell or share personal information.
- Sensitive personal information. We do not collect sensitive personal information and therefore do not use or disclose it for purposes that would require a “Limit the Use of My Sensitive Personal Information” link.
- Shine the Light (Cal. Civ. Code § 1798.83). We do not disclose personal information to third parties for those third parties’ own direct marketing purposes.
- Minors. We do not sell or share the personal information of consumers under sixteen.
- Metrics. Where required, we will make privacy request metrics available on request.
12.3 Other states with comprehensive privacy laws
Residents of Colorado, Connecticut, Virginia, Texas, Oregon, Montana, Delaware, Iowa, Nebraska, New Hampshire, New Jersey, Tennessee, Minnesota, Maryland, Indiana, Kentucky, Rhode Island, Utah, and other states whose comprehensive privacy laws are or become effective have the rights described in Section 11, including access, correction, deletion, portability, opt-out, and, where their state provides it, appeal.
Consistent with the data minimization standard adopted in Maryland and reflected in other state laws, we limit collection to what is reasonably necessary and proportionate to provide the services you request.
We do not process personal information in a manner that would require a data protection assessment under these laws. Should that change, we will conduct an assessment before beginning the processing.
12.4 Nevada
Nevada residents may submit a verified request that we not sell certain covered information. The Firm does not sell covered information as defined by Nevada law.
13. Communications and Marketing
- Email. We send newsletters and insights only to individuals who opt in. Every marketing email includes a working unsubscribe link, our physical mailing address, and an accurate subject line, consistent with the CAN-SPAM Act. Unsubscribe requests are honored promptly and do not affect transactional or engagement-related messages.
- Telephone. We use telephone numbers you provide to respond to your inquiry or coordinate an appointment. We do not make telemarketing calls, use automatic telephone dialing systems, or send marketing text messages. Should we introduce SMS communications, we will obtain prior express written consent as required by the Telephone Consumer Protection Act.
14. Data Security
The Firm maintains administrative, technical, and physical safeguards designed to protect personal information, including as of the Effective Date: TLS 1.2+ encryption in transit, AES-256 encryption at rest on core systems, authenticator-app or hardware-token MFA enforced on all business systems that store or process client data (excluding legacy systems noted in the Firm’s MFA coverage report), role-based access restricted to personnel with a legitimate need and reviewed quarterly with audit logging, vendor due diligence and contractual security commitments, encrypted geographically-redundant backups tested quarterly, and a documented and tested incident response plan. However, no security measure is completely secure, and THE FIRM EXPRESSLY DISCLAIMS ANY WARRANTY OF UNBREAKABLE SECURITY OR FREEDOM FROM BREACH; the Firm’s liability for any breach, unauthorized access, or data loss shall not exceed the lesser of fees paid in the prior twelve months or $10,000, with no liability for indirect, consequential, or punitive damages, and the Firm shall not be liable for breaches caused by client-side failures, social engineering, zero-day vulnerabilities, state-sponsored attacks, or vendor breaches where reasonable due diligence was exercised. If the Firm becomes aware of a breach triggering notification obligations under applicable law, it shall notify affected individuals and regulators within the deadlines prescribed by the governing jurisdiction (subject to law enforcement delay requests) and offer credit monitoring where required by law or insurance. The Firm shall, upon regulatory or client request, produce a redacted attestation of its then-current MFA coverage, encryption status, and access logs for the relevant period, but this Policy reflects controls as of the Effective Date and is updated annually, not a static guarantee of future capabilities.
15. Children’s Privacy
The Site is directed to businesses and professionals and is not intended for children. We do not knowingly collect personal information from anyone under sixteen, and we do not knowingly collect personal information from children under thirteen in violation of the Children’s Online Privacy Protection Act. If you believe a child has provided us with information, contact us and we will delete it.
16. Job Applicants
If you apply for a role with the Firm, we collect and use your application materials solely to evaluate your candidacy, communicate with you about the role, and comply with employment and equal opportunity recordkeeping obligations. We do not use automated decision-making to screen candidates without human review. We retain application materials for up to twelve months unless you ask us to retain them longer. Applicants in California and other states have the rights described in Section 11 with respect to this information.
17. Third-Party Links, Social Media, and Visitors Outside the United States
The Site links to third-party platforms, including our profiles on Facebook, X (formerly Twitter), and Instagram. We are not responsible for the privacy practices of those platforms, and their own policies govern your interactions with them.
Our services are directed to organizations in the United States, and personal information we collect is stored and processed in the United States. If you access the Site from outside the United States, you understand that your information will be transferred to and processed in the United States, where data protection laws may differ from those of your jurisdiction. We do not target our services to individuals in the European Economic Area, the United Kingdom, or Switzerland. If you are located in one of those jurisdictions and have questions about your data, contact us and we will address your request.
18. Changes to This Policy
We may update this Policy to reflect changes in our practices, technology, or applicable law, and we review it at least annually. When we update it, we will revise the “Last Updated” date above. If the changes are material, we will provide prominent notice on the Site and, where we hold your email address and the change affects you, by email. Your continued use of the Site after the effective date of an update constitutes acceptance of the revised Policy.
Prior versions of this Policy are available on written request.
19. Contact Us
Questions, requests, or complaints regarding this Policy or our data practices may be directed to:
Sentinel Strategy Group LLC
Attn: Privacy
205 N Michigan Ave, Suite 810
Chicago, IL 60601
United States
Email: info@sentinelstrategygroup.org
Subject line for rights requests: “Privacy Request”
We aim to respond to privacy inquiries within two business days and to substantive rights requests within the timeframes set out in Section 11.
20. Legal Notices
No legal advice. Sentinel Strategy Group LLC is a consulting practice. Nothing on the Site, in this Policy, or in our communications constitutes legal advice, and no attorney-client relationship is created by visiting the Site, submitting a form, subscribing to our communications, or engaging the Firm for consulting services. Our services do not include the practice of law, and clients should retain qualified counsel for legal advice regarding their specific circumstances.
No confidential relationship through the Site. Information submitted through our web forms is not treated as confidential or privileged until a written engagement agreement is in place. Please do not send confidential or sensitive information through the Site.
21. General Terms
Non-waiver of statutory rights. Nothing in this Policy, including the limitations of liability in Sections 8 and 14, waives, limits, or disclaims any right or remedy that cannot be waived, limited, or disclaimed under applicable law. This includes, without limitation, rights under the California Consumer Privacy Act, the Illinois Biometric Information Privacy Act, and the consumer privacy and data breach notification statutes of any state. Where any limitation in this Policy conflicts with a non-waivable statutory right, the statutory right controls as to that individual and that claim only.
Relationship to engagement agreements. For clients, the executed engagement agreement, together with any data processing addendum, governs the treatment of client data and the allocation of risk between the parties. Where this Policy and an engagement agreement address the same subject, the engagement agreement controls as between the Firm and that client. This Policy does not create contractual rights for clients beyond those in their engagement agreement.
Third parties. This Policy is a notice of the Firm’s practices. Except as required by law, it does not create third-party beneficiary rights.
Severability. If any provision of this Policy is held unenforceable, that provision will be modified to the minimum extent necessary to make it enforceable, or severed, and the remaining provisions will continue in full force and effect.
Governing law. This Policy and any dispute arising from it are governed by the laws of the State of Illinois, without regard to its conflict of laws principles, except where the law of another jurisdiction applies by operation of a non-waivable consumer protection or privacy statute.
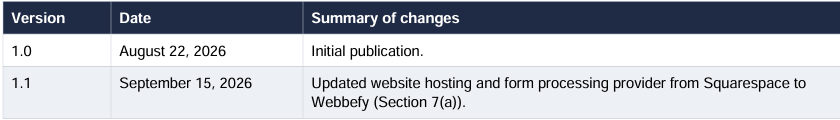
Version History